chore(deps): refresh packages, Node 24.21, and security overrides - #166
Merged
Merged
Conversation


Bump runtime/tooling pins and patch audit findings via overrides for
js-yaml and adm-zip while keeping ESLint 9 / TypeScript 6 / Node 24.

|
Important Review skippedBot user detected. To trigger a single review, invoke the ⚙️ Run configurationConfiguration used: defaults Review profile: CHILL Plan: Advanced Run ID: You can disable this status message by setting the Use the checkbox below for a quick retry:
Thanks for using CodeRabbit! It's free for OSS, and your support helps us grow. If you like it, consider giving us a shout-out. Comment |

Lighthouse results
Updated automatically by CI. |

95gabor
approved these changes
Sep 14, 2026

95gabor
marked this pull request as ready for review
September 14, 2026 07:28
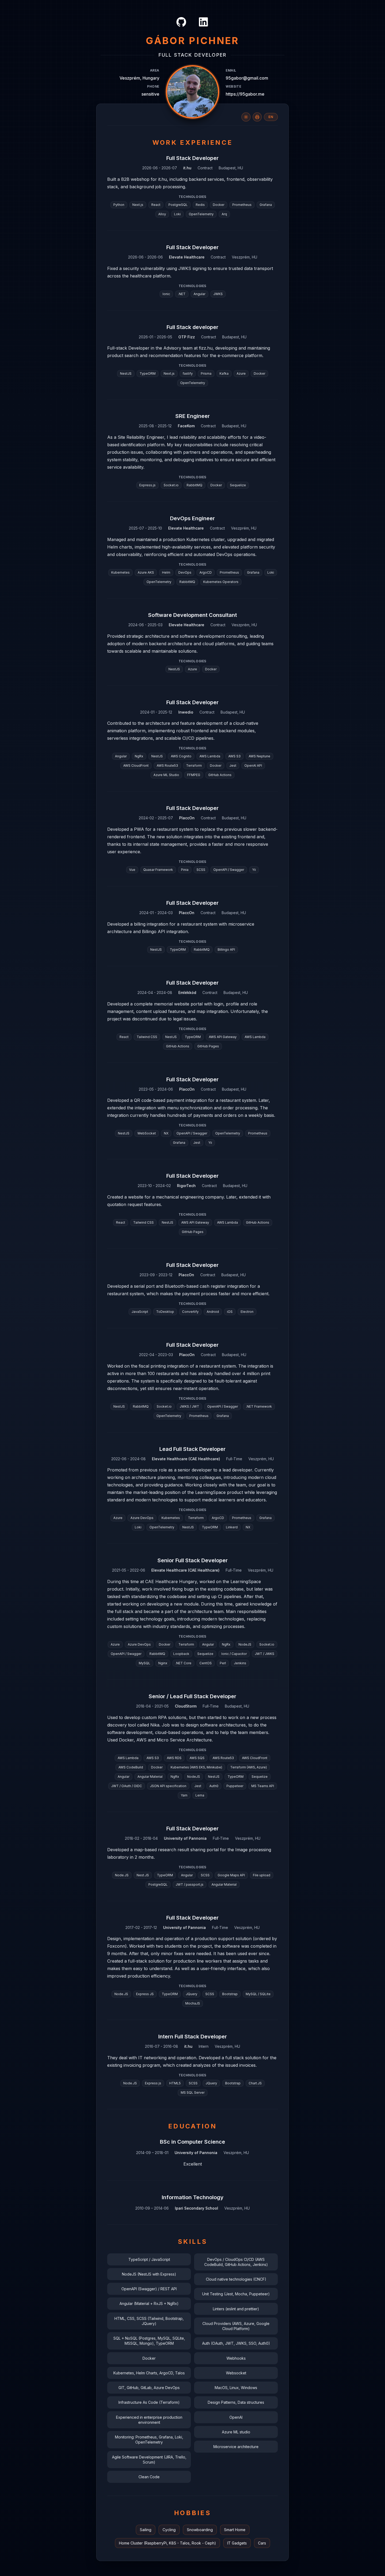
Latest full-page screenshot
|

This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment
2 participants


Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Summary
Weekly dependency/security maintenance (2026-09-14).
Package updates
next/eslint-config-next16.3.4 → 16.3.5react/react-dom19.2.8 → 19.3.0@types/react/@types/react-dom→ 19.3.0@supabase/supabase-js2.115.0 → 2.116.0next-intl4.14.2 → 4.14.4lucide-react1.41.0 → 1.45.0tailwind-merge3.6.0 → 3.7.0@percy/cli1.32.8 → 1.32.9lint-staged17.5.0 → 17.5.1supabase2.116.0 → 2.117.0yaml2.9.0 → 2.9.1@types/node24.13.3 → 24.13.4 (stays on Node 24 types)pnpm12.3.4 → 12.4.1Runtime / Docker
24.20.0→24.21.0(.nvmrc,engines, node-bootstrap,Dockerfilenode:24.21.0-alpine3.24)1.31.5-alpine3.24-slim(latest)Security overrides
js-yaml@4.3.2(GHSA-2883-xcg3-v3hh),adm-zip@0.6.1(GHSA-vwc7-r8mq-g2x9)browserslist@4.28.9,fast-uri@3.1.7,fast-xml-parser@5.11.1,uuid@11.1.1(still required after refresh)pnpm audit: cleanHeld majors (intentional)
@types/node24 (not 26), Node 24 LTS (not 26 Current)GitHub Actions
Already on latest major pins (
checkout/setup-node/upload-artifactv7, Pages v5/v6, Docker v4/v6/v7,treosh/lighthouse-ci-actionv12). No workflow changes needed.Validation
pnpm install --frozen-lockfilepnpm audit— no known vulnerabilitiespnpm run lint— pass (existing warnings only)pnpm run typecheck— passSuperseded Dependabot PRs (please close)
build(deps): bump node ... to 26.8.1-alpine3.24— rejected; stay on Node 24 LTSbuild(deps-dev): bump @types/node ... to 26.4.0— rejected; keep@types/nodeon 24 while runtime is Node 24(
ghis read-only in this automation, so these could not be closed automatically.)